


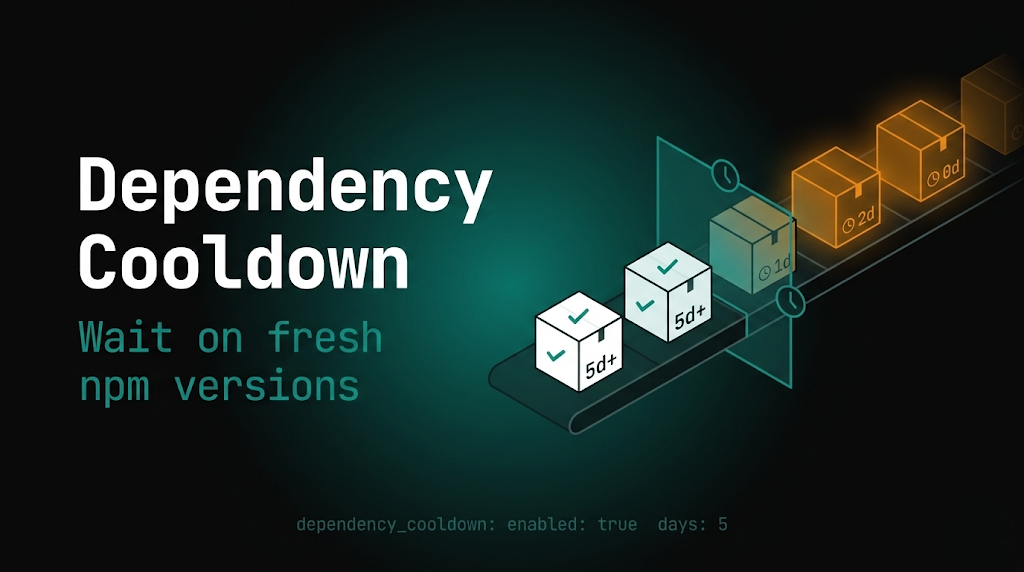
PMG dependency cooldown: wait on fresh npm versions
Package Manager Guard (PMG) blocks malicious installs and now supports dependency cooldown, a configurable window that hides brand-new npm versions during resolution so installs prefer older,...
Follow for the latest updates and insights on
open source security & engineering.
Package Manager Guard (PMG) blocks malicious installs and now supports dependency cooldown, a configurable window that hides brand-new npm versions during resolution so installs prefer older,...

js-logger-pack spent three weeks on npm evolving from a probe into a full infostealer and then a binary dropper. Early versions installed an SSH backdoor, hijacked Telegram sessions, drained 27...

A dependency confusion campaign by npm user victim59 targets at least three organizations through scoped packages @genoma-ui/components, @needl-ai/common, and rrweb-v1. The packages use install hooks...
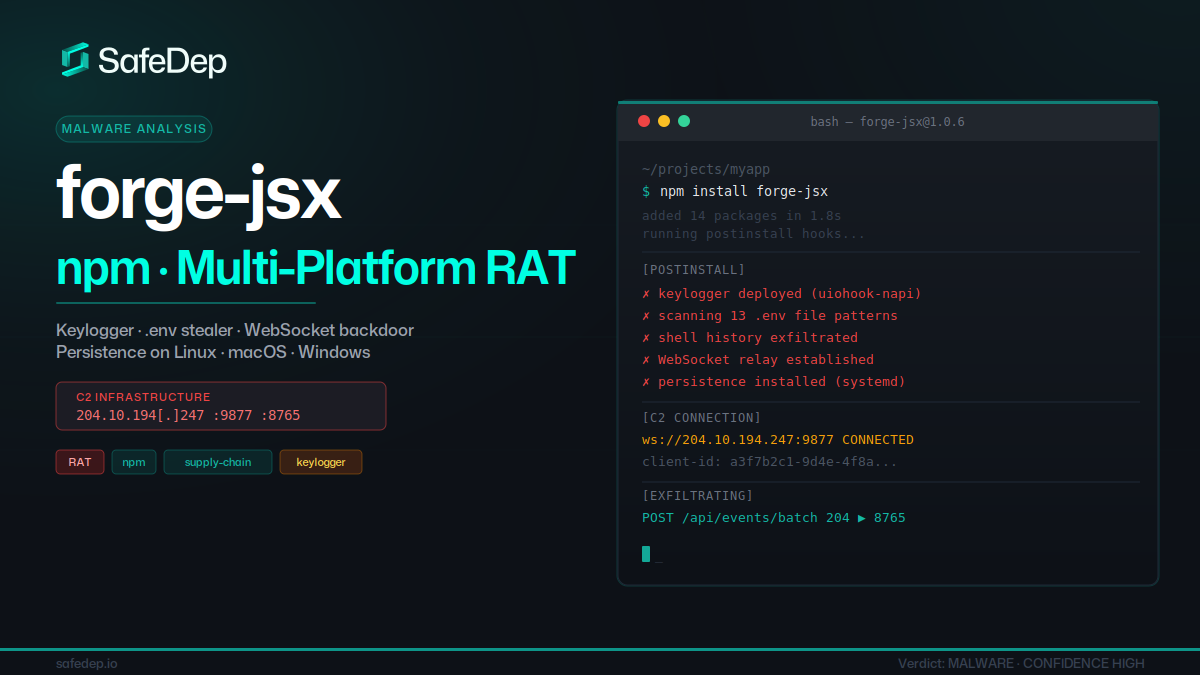
forge-jsx poses as an Autodesk Forge SDK on npm. On install it deploys a system-wide keylogger, recursive .env file scanner, shell history exfiltrator, and a WebSocket-based remote filesystem...

dom-utils-lite and centralogger on npm inject attacker SSH keys into ~/.ssh/authorized_keys and exfiltrate server metadata to Supabase-hosted C2 infrastructure, granting persistent remote access.

Start free with open source tools on your machine. Scale to a unified platform for your organization.
SafeDep keeps analytics anonymous and cookie-free until you opt in. Accepting helps us understand product usage and improve your experience. Privacy Policy
Choose what you share. You can change this anytime from the footer.
